Vendor onboarding is more than filling out a registration form. Depending on the relationship, an organization may need business details, tax information, payment instructions, insurance evidence, contracts, certifications, security information, operational requirements, and internal approvals. The exact requirements should be based on the vendor’s category, risk, geography, services, data access, and applicable organizational policies.
This guide explains how to design and use a vendor onboarding template from the initial request through approval and activation. It also compares common formats, explains the fields worth collecting, provides practical examples, shows how to build a checklist, and outlines a practical solution that can work for a small business or scale into a more controlled procurement workflow.
What Is a Vendor Onboarding Template?
A vendor onboarding template is a standardized document, spreadsheet, form, or workflow used to collect and organize the information required to establish a new supplier relationship. It provides a consistent structure so employees know what to request, vendors know what to provide, and reviewers know what must be checked before activation.
The best templates separate information collection from verification. A vendor may submit a tax document, certificate, bank letter, or company profile, but submission alone does not prove that the information has been reviewed. A useful template therefore includes fields for status, reviewer, verification date, exceptions, missing documents, and follow-up actions.
A template can also create a common language between departments. Procurement may focus on supplier qualification, finance on payment readiness, legal on agreements, IT on access, security on data exposure, and operations on delivery requirements. The template connects those responsibilities without requiring every team to maintain a separate vendor record.
Modern onboarding workflows often begin with an internal request, followed by vendor data collection, document review, risk assessment, approval, system setup, and operational activation. This sequence can be adjusted for the organization, but the central principle remains the same: collect enough reliable information to make an informed decision and establish the vendor correctly.
A template should therefore be viewed as a control mechanism rather than merely a form. It helps prevent incomplete records, duplicate vendor creation, unclear ownership, payment delays, expired documents, and undocumented exceptions. It also creates an auditable trail showing what was requested, what was received, who reviewed it, and what decision was made.

Why the Template Matters
The main benefit of a standardized onboarding process is consistency. When every new supplier follows the same baseline path, the organization is less dependent on individual employees remembering which information to request or which department needs to approve it.
Consistency is particularly important when vendor volume increases. A process that works for five suppliers may become difficult to control when dozens or hundreds of vendors are being added throughout the year. A template creates a reusable starting point that can be refined as the organization’s needs evolve.
Another advantage is faster identification of missing information. Instead of discovering during the first invoice that the legal name is incorrect or the payment details are incomplete, the organization can identify those gaps before the vendor becomes active.
Templates also make handoffs easier. If procurement completes the initial review and finance takes responsibility for payment setup, finance can see exactly what has already been collected. This reduces repeated questions and prevents information from becoming trapped in individual inboxes.
Finally, a template creates a useful historical record. If the vendor is reviewed again during renewal, an audit, a change of banking details, or a performance review, the organization can use the original onboarding record as a baseline rather than starting from scratch.
Core Components of a Vendor Onboarding Template
A strong template should collect only information that has a clear business purpose. Requesting every conceivable document creates friction for suppliers and increases the amount of information internal teams must maintain. The better approach is to establish a baseline set of fields and then add conditional requirements for higher-risk or specialized vendors.
The first section normally identifies the vendor. Useful fields include legal business name, trading name if applicable, business structure, registration location, business address, website, primary contact, finance contact, and operational contact. Keeping these fields standardized makes downstream vendor-master records cleaner.
The second section should capture the reason the vendor is being onboarded. Record the requesting department, internal business owner, category of goods or services, expected start date, anticipated relationship type, and relevant purchase or project reference. This context helps reviewers understand why the vendor is being added.
The third section covers documentation. Instead of simply asking vendors to upload files, the template should identify the document type, whether it is required, whether it was received, whether it was verified, the verification date, and the responsible reviewer. This turns a document collection exercise into a controlled review process.
The final core sections typically cover financial setup, contracts, risk and compliance, technology or security requirements where applicable, internal approvals, and activation. Not every vendor needs every section, so conditional logic or risk tiers can make the process more efficient.

1. Vendor Identity and Contact Information
Begin with the vendor’s official business identity. The legal name should be recorded separately from any brand or trading name because contracts, tax records, invoices, and vendor-master systems may use the legal entity name.
Record the primary contact and distinguish that person from finance, billing, sales, technical, and emergency contacts when those roles are relevant. A single contact may be appropriate for a small supplier, while larger suppliers often require several points of contact.
Location information should also be structured consistently. Capture the registered address, operating location when relevant, country or region of registration, and service or delivery locations if the relationship depends on geography.
Where business registration information is important, provide fields for registration number, issuing authority, registration date, and verification status. The organization should verify these details against an appropriate authoritative source when its policy or risk assessment requires it.
Keep the identity section separate from sensitive payment information. This makes the form easier to review and reduces unnecessary exposure of financial information to employees who do not need access to it.

2. Products, Services, and Business Context
A vendor record is more useful when it explains what the supplier actually provides. A short description of the product or service helps procurement, finance, operations, and risk reviewers understand why the relationship exists.
Include a category or service type field that can be standardized through a dropdown where practical. Consistent categories make later reporting easier and can also determine which additional questions or documents should appear.
Record the internal business owner because onboarding should not become an administrative task with no accountable stakeholder. The business owner can clarify the commercial purpose, confirm operational requirements, and help resolve questions raised during review.
Expected spend or relationship value can also be useful for internal prioritization. It does not need to be exact at the earliest stage; an estimated range may be sufficient to determine the appropriate approval route.
For service providers, note whether the vendor will work on company premises, interact with customers, access systems, handle confidential information, or use subcontractors. These factors can change the risk profile and therefore the onboarding requirements.

Financial, Tax, and Payment Information
Payment setup deserves careful treatment because errors can delay legitimate payments and create opportunities for fraud. A template should therefore distinguish between information supplied by the vendor and information independently verified by the organization.
Typical financial fields can include payment currency, preferred payment method, billing contact, invoice submission method, payment terms, and tax documentation status. The exact tax fields depend on the countries and transaction types involved.
Banking information should be collected through a controlled process appropriate to the organization’s security requirements. Access to full bank account information should be limited to people who need it, and changes to existing payment details should receive heightened verification.
Payment terms should be consistent with the commercial agreement. If the template records a payment term that differs from the signed contract or purchase arrangement, the discrepancy should be resolved before activation rather than silently changing one record to match another.
For international suppliers, the template may require additional tax residency, currency, intermediary-bank, or local documentation fields. These should be included only when relevant and should be reviewed by the appropriate finance or tax function rather than treated as universal requirements.

Tax Documents Should Be Country-Specific
Tax documentation is an area where generic templates can easily become misleading. A document appropriate for one country may be irrelevant in another, and requirements can vary according to the vendor’s legal structure, location, transaction type, and tax status.
For example, a U.S.-based process may request a taxpayer identification form where appropriate, while another jurisdiction may use different registration or tax documentation. The template should therefore use conditional questions instead of presenting one country’s document as a universal vendor requirement.
Record whether the relevant document was requested, received, reviewed, and accepted. If an exception is approved, capture the decision and responsible approver rather than simply marking the document as complete.
Do not store unnecessary sensitive information merely because a template makes it possible. A good onboarding process follows data-minimization principles and collects information that is genuinely necessary for the business purpose.
Where tax treatment is uncertain, the template should route the issue to the organization’s finance or tax specialists. A checklist can identify a question, but it should not replace professional judgment about tax obligations.

Compliance, Due Diligence, and Risk Assessment
Vendor onboarding is also a risk-management activity. The objective is not to make every supplier complete the same enormous questionnaire; it is to apply controls that are proportionate to the potential consequences of the relationship.
A low-risk supplier providing ordinary office supplies may require a simpler review than a technology provider handling confidential information. A contractor working at a physical site may require safety or insurance evidence that would make no sense for a remote professional-services vendor.
Risk questions can cover regulatory exposure, information security, access to company systems, handling of sensitive information, operational dependency, geographic exposure, subcontracting, business continuity, insurance, and other factors relevant to the organization’s environment.
Due diligence should distinguish evidence from assertions. A vendor saying that it maintains a particular control is different from providing documentation or an independently verifiable record. The appropriate evidence standard should be determined by the risk and internal policy.
The result should be easy to understand. A template can assign a risk tier such as low, medium, or high, but the definitions should be documented internally so that different reviewers apply the categories consistently.
Document Verification Is Different From Document Collection
One of the most common weaknesses in onboarding is treating an uploaded document as automatically verified. A file can be present while still being expired, incomplete, inconsistent with other records, or unrelated to the entity being onboarded.
The template should therefore provide a verification status separate from a received status. Useful values might include Not requested, Requested, Received, Under review, Verified, Rejected, and Not applicable.
Expiration dates should be recorded for documents that become invalid over time. The record can then support later renewal reminders rather than requiring staff to rediscover expiration dates when a transaction is already underway.
Reviewers should document material discrepancies. If the legal name differs between two documents, for example, the record should show what was investigated and how the discrepancy was resolved.
For high-risk relationships, independent verification may be appropriate. The template should identify the source checked, date checked, reviewer, and outcome, while avoiding the unnecessary storage of sensitive evidence.

Contract and Approval Controls
The onboarding record should connect the vendor to the commercial agreement that governs the relationship. Depending on the transaction, this might be a master agreement, statement of work, purchase agreement, order form, or another approved contract structure.
Important fields can include contract owner, agreement type, signature status, effective date, expiration date, renewal terms, and storage location. The template should not attempt to replace the contract itself; it should make the contract’s status visible to the teams managing the vendor.
Approval routing should be based on the organization’s delegation of authority and internal policies. A template can identify who must approve a vendor, but it should not claim that a particular approval level is universally required.
Consider separating business approval from compliance approval. The person who wants to use a vendor may confirm the business need, while another function may independently review legal, financial, security, or risk considerations.
Where multiple approvals are required, record each one separately. This is more useful than a single checkbox because it shows exactly which control has been completed and which approval remains outstanding.

Approval Routing Example
Imagine a company wants to onboard a software provider that will process internal customer information. The business owner submits the request and identifies the service category, expected spend, and intended users.
Procurement confirms that the supplier is appropriate for the category and checks the commercial information. Finance reviews payment setup and tax documentation. Legal reviews the agreement where required.
Because the software involves company information, the security or privacy team may receive additional questions. The vendor may need to provide evidence relevant to the organization’s established security requirements.
Each review is recorded as a separate task with an owner and status. A missing item does not disappear into email because the template shows exactly what remains unresolved.
Only after the required approvals are complete should the vendor move to the organization’s activation stage. This prevents an employee from treating an incomplete intake record as permission to begin purchasing.

How to Build a Vendor Onboarding Template Step by Step
Start by mapping the current onboarding process before designing the document. Interview the people who request vendors, collect information, review documentation, create vendor records, approve contracts, and process payments.
Write down every handoff and identify where delays occur. Common problems include missing documents, unclear ownership, duplicate data entry, inconsistent approval thresholds, and uncertainty about when a vendor is actually considered active.
Next, divide requirements into baseline and conditional categories. Baseline requirements should apply to most vendors. Conditional requirements should appear only when triggered by category, risk, geography, data access, location, or other relevant characteristics.
Then define status values and ownership. A task without an owner is difficult to manage, while a task without a status makes progress invisible. The combination of owner, status, due date, and evidence creates a useful operational record.
Finally, test the template with several hypothetical vendor types. Try a low-risk supplier, a professional-services provider, a software vendor, and a contractor with site access. If every scenario produces the same unnecessary workload, the template probably needs more conditional logic.

Recommended Field Structure
A practical spreadsheet can use columns such as Vendor ID, Legal Name, Category, Business Owner, Primary Contact, Risk Tier, Required Documents, Document Status, Contract Status, Finance Status, Security Status, Approval Status, Target Activation Date, and Notes.
A separate document register can provide more detail. Each row can represent one document, with columns for document type, required status, received date, expiration date, reviewer, verification result, and follow-up action.
A task register can then track internal actions. Examples include procurement review, legal review, finance setup, security review, system creation, purchase-order readiness, and business-owner confirmation.
Do not overload one worksheet with every detail if doing so makes it difficult to use. A workbook with a summary sheet, vendor information sheet, document register, and approval tracker is often easier to maintain than one extremely wide table.
For smaller organizations, one well-designed sheet may be enough. The right design is the simplest structure that provides reliable control over the information and decisions the organization actually needs.

Choosing Between Excel, Word, PDF, and Online Forms
The format should match the job. A spreadsheet is useful when teams need structured rows, sorting, filtering, status tracking, formulas, and reporting. It is particularly practical for maintaining a vendor register or monitoring many onboarding cases.
A word-processing document is better suited to a narrative questionnaire, policy document, printable form, or supplier-facing document where page layout matters more than tabular analysis.
A PDF is useful when a stable, printable representation of a completed document is needed. However, a PDF is not automatically a good system of record. Organizations should decide where the authoritative vendor data will live rather than allowing multiple PDF copies to become inconsistent.
An online form can improve the collection experience by guiding the vendor through questions, using required fields, validating entries, and showing conditional questions. Responses can then be routed into a controlled workflow.
The most effective approach may combine formats. For example, an online form can collect information, a workflow can manage approvals, and a spreadsheet or vendor-management system can maintain the final operational record.

When Excel Is the Best Starting Point
Excel is often a sensible starting point for organizations that need structure without immediately implementing specialized procurement software. It supports filters, dropdown lists, formulas, conditional formatting, tables, and summary calculations.
A basic workbook can include one row per vendor and additional tabs for documents and approvals. This approach works especially well when the number of active onboarding cases is manageable and the organization already has clear ownership rules.
However, spreadsheets should not become a substitute for access controls or formal workflow management. If many people edit the same file, sensitive information is included, or several versions circulate by email, the spreadsheet can create more risk than it removes.
Use controlled storage, clearly defined editing rights, consistent naming, and a documented owner. Establish which sheet is authoritative and how completed records are archived.
As volume grows, the organization can migrate the same field structure into a database, procurement platform, or form workflow. A well-designed spreadsheet therefore becomes a useful prototype for a more mature process rather than wasted work.

Using a Vendor Onboarding Checklist Template
A checklist is the operational layer of the onboarding process. While the main form gathers information, the checklist tells the organization what actions must occur before the vendor is activated.
Each checklist item should have a clear completion condition. “Review documents” is vague; “Confirm required documents are received, valid, and reviewed” is easier to interpret. Where appropriate, the checklist should specify what evidence demonstrates completion.
Assign each item to a role rather than relying on a generic team name. A named role such as Procurement Owner, Finance Reviewer, Legal Reviewer, or Security Reviewer creates clearer accountability while remaining reusable across employees.
Use statuses that reflect actual progress. A simple structure might include Not Started, In Progress, Blocked, Complete, and Not Applicable. Avoid using Complete when an item is merely waiting for someone else.
Include a notes or exception field. This provides context when a vendor has an approved exception, a document is unavailable for a legitimate reason, or a reviewer needs another team to resolve an issue.

Sample Checklist
Pre-onboarding: Confirm business need, identify the internal owner, define the vendor category, estimate the relationship scope, and determine the appropriate risk tier.
Vendor information: Collect legal name, business address, contacts, registration information, service description, and other baseline identity fields relevant to the relationship.
Documentation: Request applicable tax, insurance, certifications, business registration, security, compliance, and contractual documents based on the vendor’s profile.
Review: Verify the required evidence, record discrepancies, confirm contract status, complete appropriate risk reviews, and obtain the necessary internal approvals.
Activation: Create or update the vendor record, confirm payment readiness, establish required system access, communicate operational procedures, and record the activation date.

Vendor Onboarding Form Design
A vendor onboarding form should be easy for the supplier to understand. Questions should use plain language, explain what information is expected, and avoid asking for details that do not affect the onboarding decision.
Group related questions into logical sections. Business identity, contacts, products or services, financial information, compliance, documentation, and declarations should not appear as one long unstructured list.
Use appropriate field types. Dropdowns are useful for standardized categories, date fields reduce inconsistent date formats, checkboxes work for simple confirmations, and file uploads can organize supporting evidence.
Conditional questions are especially valuable. If a vendor indicates that it will access company systems, the form can present additional security questions. If it does not, those questions can remain hidden.
Before publishing a form, test it from the vendor’s perspective. Check whether required fields are understandable, whether instructions are clear, whether uploads work, and whether the information collected can be transferred cleanly into the internal vendor record.

Example Form Sections
Section A — Company information: Legal business name, trading name, business structure, registration location, business address, website, and company contact information.
Section B — Contacts: Primary contact, sales contact, billing contact, technical contact, and emergency contact where relevant to the relationship.
Section C — Services: Products or services provided, service category, operating locations, expected start date, and a short description of the relationship.
Section D — Finance: Billing details, payment method, currency, applicable tax documentation, and other information required by the organization’s finance process.
Section E — Compliance: Applicable certifications, insurance, regulatory information, security questions, subcontractor information, declarations, and document uploads based on risk and category.

Data Quality and Vendor Master Management
Onboarding quality directly affects vendor-master quality. If the same supplier appears under different names, addresses, or identifiers, procurement and finance teams may struggle to distinguish legitimate changes from duplicate records.
Establish validation rules for important fields. For example, require a legal name before approval, use consistent country and currency values, and prevent the same internal vendor identifier from being assigned twice.
Duplicate detection should be part of the process before a new record is created. Search existing vendor records using several relevant identifiers rather than relying only on an exact company-name match.
Changes to important information should follow a controlled update process. Banking changes, legal-name changes, ownership changes, or major address changes may require evidence and additional verification depending on the organization’s controls.
Maintain a clear distinction between the vendor’s submitted information and the organization’s internal classification. A vendor can provide its company category, but the procurement team may assign the official internal category or risk tier.

Using Spreadsheets for Data Analysis
Once onboarding data is structured, the organization can analyze the process itself. Useful measures include the number of vendors in each status, the number of incomplete records, average time between request and activation, and the most common reasons for delays.
These measures should be used for process improvement rather than as unsupported claims about vendor performance. For example, if many cases remain blocked because insurance documents are missing, the organization can improve the initial communication or change when the document is requested.
Category-level analysis can reveal whether particular vendor types consistently require additional review. This can help the organization create better conditional questions and more accurate risk tiers.
Trend analysis can also show whether onboarding workload is growing. If the number of requests increases while staffing remains constant, automation or workflow redesign may become more valuable.
The goal is not to measure everything. A small set of reliable operational measures is more useful than a dashboard full of metrics that nobody reviews or understands.

How to Make Onboarding Faster Without Weakening Controls
Speed and control are not necessarily opposites. Much of the time lost during onboarding comes from unclear requirements, repeated questions, missing ownership, and unnecessary manual handoffs rather than from the review itself.
Start by defining a minimum information set. Vendors should know exactly what they need to provide, while internal teams should know exactly what they are responsible for reviewing.
Use parallel reviews when the organization’s controls allow it. Legal, finance, security, and procurement do not always need to wait for one another to begin their work. Running appropriate reviews concurrently can reduce idle time.
Automate reminders for incomplete tasks, but do not automate judgment that requires a qualified reviewer. A reminder can tell a supplier that a document is missing; it should not decide that an ambiguous document is acceptable.
Finally, create escalation rules for blocked cases. A vendor should not remain “in progress” indefinitely without someone knowing why. A blocked status should identify the issue, owner, and next action.

Common Onboarding Bottlenecks
Incomplete forms: Reduce this problem with required fields, clear instructions, and category-specific questions rather than sending every vendor the same enormous questionnaire.
Unclear ownership: Assign an accountable internal owner and individual review responsibilities. A shared inbox alone is rarely enough to establish accountability.
Serial approvals: Where policy permits, perform independent reviews concurrently rather than routing every case through a single long chain.
Repeated data entry: Design the form so information can be transferred into the vendor master or downstream system without unnecessary retyping.
Unresolved exceptions: Give exceptions an explicit status and approval path. Do not hide unresolved issues by marking the overall onboarding case as complete.

Common Mistakes to Avoid
The first mistake is creating a template that tries to cover every imaginable risk. Excessive requirements increase supplier effort and overwhelm internal reviewers. Start with a practical baseline and add requirements only when they are justified.
The second mistake is failing to define what “complete” means. A checkbox labeled Complete is meaningless if one reviewer interprets it as “document received” and another interprets it as “document independently verified.” Each important status should have a clear definition.
The third mistake is collecting sensitive information in places where it does not belong. If an employee does not need to see banking information, tax identifiers, or confidential documents, the process should not expose those details unnecessarily.
The fourth mistake is forgetting the post-onboarding stage. A vendor record should remain useful after activation. Important dates, performance reviews, contract renewals, document expirations, and material changes may need to be tracked later.
The fifth mistake is treating the template as permanent. Business requirements change, systems change, and risk priorities change. Review the template periodically and remove fields that no longer serve a useful purpose.

Security and Privacy Considerations
A vendor onboarding process can contain commercially sensitive and personally identifiable information. The template should therefore be designed with access control, secure storage, appropriate retention, and controlled sharing in mind.
Do not email sensitive financial information simply because email is convenient. Use the organization’s approved secure method for collecting and storing sensitive documents.
Limit access according to role. Procurement may need broad visibility into onboarding status, while a finance team may need access to payment information and a security team may need access to security questionnaires.
Keep an audit trail for important changes. When a vendor’s status changes from rejected to approved, or when a key document is replaced, the record should preserve enough history to explain what happened.
Retention should also be deliberate. Organizations should define how long vendor records and supporting documents are retained according to their policies, legal obligations, contractual needs, and applicable regulations.

Practical Examples by Vendor Type
A local office-supply vendor may need a relatively simple onboarding path: business identity, contact information, tax or billing details, payment setup, commercial terms, and basic internal approval. There may be little reason to ask for extensive security documentation.
A professional-services firm may require contract information, insurance evidence, payment details, tax documentation, confidentiality terms, and information about the people delivering the service. The business owner may also need to confirm the scope and expected deliverables.
A software provider may require a more detailed review if it processes company information or connects to internal systems. Questions about data access, security controls, integration, user access, incident handling, and contract terms may become relevant.
A contractor working at a physical facility may need additional operational documentation. Depending on the work, the organization could require evidence related to insurance, qualifications, site access, safety procedures, or other controls.
The key lesson is that the same vendor onboarding template can support all four scenarios if it uses a common baseline plus conditional requirements. This is usually more practical than maintaining an entirely separate process for every supplier type.

Hypothetical Example: A New Software Vendor
Suppose a marketing department wants to use a new cloud-based analytics service. The department submits an internal request and identifies the business owner, expected users, service category, estimated spend, and intended start date.
The procurement reviewer checks whether an existing vendor can already provide the required service and confirms that the proposed supplier belongs in the appropriate category. The vendor then completes the information form.
Finance reviews payment and tax information, while legal reviews the agreement where required. Because the service processes company information, the appropriate security or privacy review is also triggered.
The vendor receives a request for any missing evidence. Each reviewer records a status rather than communicating completion only through email. The business owner can see that the case is waiting for one outstanding review.
After all required controls are complete, the vendor record is created, the necessary operational setup is performed, and the activation date is recorded. The onboarding record remains available for later contract or performance reviews.

Vendor Onboarding Documentation and Reporting
Good documentation should make the vendor relationship understandable to someone who was not involved in the original onboarding. A reviewer should be able to identify the vendor, understand the business purpose, see the relevant evidence, and determine who approved the relationship.
For reporting, separate operational facts from judgments. “Insurance certificate received” is a factual status. “Vendor is low risk” is a classification that should have an established methodology behind it.
Use consistent naming conventions for files and records. A logical structure might separate corporate information, contracts, financial documents, compliance evidence, security reviews, and correspondence where appropriate.
Link records to internal identifiers rather than relying on filenames alone. A vendor ID, contract ID, or purchase reference can help connect onboarding information with procurement and finance systems.
Reports should answer practical management questions: Which vendors are waiting for approval? Which cases are blocked? Which documents expire soon? Which teams have the largest review backlog? Which onboarding stages cause the most delays?

Reviewing the Template Periodically
Set a regular review cycle for the onboarding process. The frequency should reflect the organization’s size, risk environment, and rate of change rather than an arbitrary universal schedule.
Ask whether every field is still necessary. If a field is consistently unused, remove it or make it conditional. If reviewers repeatedly request information that is missing, consider adding a field or clarifying an existing question.
Review exceptions as a source of process improvement. A high number of exceptions may indicate that the policy is too rigid, the vendor population has changed, or the template does not accurately reflect real operational needs.
Check whether ownership remains accurate. New departments, reorganizations, new systems, or changes in approval authority can make an otherwise sound template obsolete.
Finally, test the complete workflow rather than reviewing only the form. The real process includes submission, document handling, approvals, vendor-master creation, payment readiness, activation, and later updates.

Practical Solution: Build a Simple, Scalable Vendor Onboarding System
The most practical solution is to build the process in layers. Start with a clear intake form, add a checklist for internal actions, create a document register for evidence, and maintain a controlled vendor record for the final approved information.
Step 1 — Define the baseline. List the information every vendor needs to provide, such as legal identity, contact information, service category, internal owner, and applicable financial details. Avoid including specialist requirements that only apply to certain vendors.
Step 2 — Define conditional requirements. Identify the triggers that require additional review. Examples include system access, sensitive information, physical site access, regulated services, significant operational dependency, international transactions, or other risk factors relevant to the organization.
Step 3 — Create ownership rules. Assign each review to an accountable role. Procurement can own supplier intake, finance can own payment readiness, legal can review contractual matters, and security can handle applicable technology or data questions.
Step 4 — Create status definitions. Decide what Requested, Received, Under Review, Verified, Blocked, Approved, Rejected, and Active mean. Publish the definitions so reviewers do not interpret statuses differently.
Step 5 — Add evidence tracking. For each required document, record whether it was received, whether it was verified, who reviewed it, and whether it has an expiration date. Keep sensitive evidence in the approved secure repository rather than unnecessarily copying it into multiple files.
Step 6 — Establish approval gates. Define which conditions must be satisfied before the vendor can be activated. The template should reflect internal delegation-of-authority and procurement policies rather than inventing universal approval thresholds.
Step 7 — Test with real-world scenarios. Run the template against several different vendor types. Remove irrelevant questions, clarify ambiguous fields, and confirm that every required handoff has an owner.
Step 8 — Measure the process. Track a small set of useful indicators such as incomplete cases, blocked cases, stage duration, and common causes of delay. Use the findings to improve the workflow instead of simply adding more fields.
Step 9 — Plan for scale. If volume increases, migrate the same logical structure into a controlled form, workflow, database, procurement platform, or vendor-management system. The field definitions and approval logic developed in the template can become the foundation for that future system.
A practical vendor onboarding template should ultimately make three things obvious: what information is needed, what has been verified, and whether the vendor is ready for the next stage. If users cannot answer those questions quickly, the template needs simplification or better workflow design.
Reference Examples
The following visual references illustrate common formats and concepts associated with spreadsheets, documents, forms, checklists, and onboarding workflows. They are examples of visual formats, not universal requirements for every organization.
vendor onboarding template excel
Source: Wikimedia Commons
vendor onboarding template pdf
Source: Wikimedia Commons
vendor onboarding template word
Source: Wikimedia Commons
vendor onboarding template free download
Source: Wikimedia Commons
vendor onboarding template free
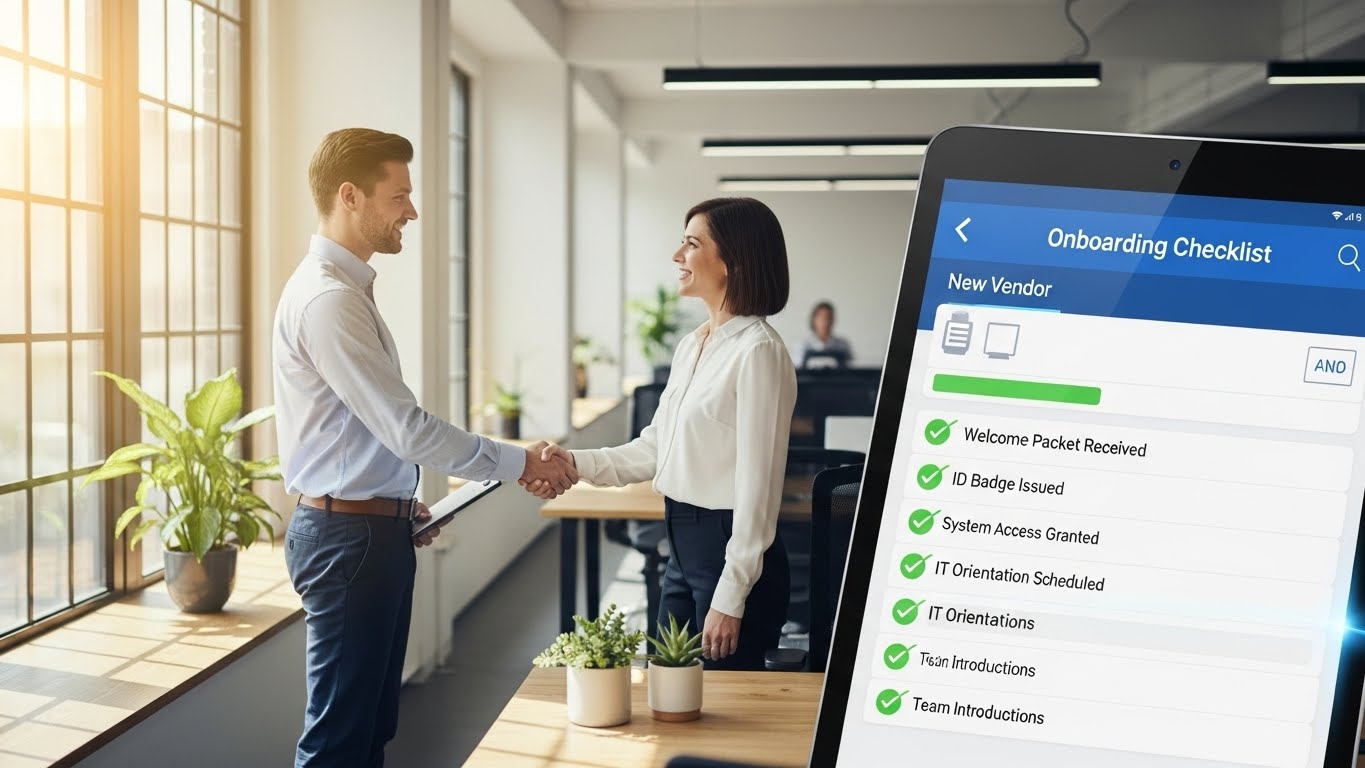
Source: VendorFi
vendor onboarding template google sheets
Source: Wikimedia Commons
vendor onboarding form template
Source: Wikimedia Commons
vendor onboarding checklist template
Source: Wikimedia Commons
new vendor onboarding template

Source: Wikimedia Commons
Frequently Asked Questions
What should a vendor onboarding template include?
At minimum, it should provide a structured way to capture vendor identity, contacts, products or services, internal ownership, applicable financial information, required documentation, review status, approvals, and activation details. Additional sections should be triggered by risk and business context.
Is a vendor onboarding template the same as a vendor registration form?
Not necessarily. A registration form primarily collects information from the vendor. Onboarding is broader because it can include internal review, due diligence, approvals, contract completion, system setup, payment readiness, and activation.
Should every vendor complete the same checklist?
A common baseline is useful, but every vendor does not necessarily need identical requirements. A risk-based structure can keep ordinary suppliers on a simple path while triggering additional reviews for vendors with greater financial, operational, security, regulatory, or data-related exposure.
Can a spreadsheet be used for vendor onboarding?
Yes. A spreadsheet can be a practical starting point when vendor volume is manageable and the organization has appropriate controls for storage, access, version management, and ownership. As complexity increases, a controlled form or workflow system may become more appropriate.
What is the difference between “received” and “verified”?
Received means the organization has obtained the requested information or document. Verified means an authorized reviewer has assessed it against the applicable requirement and recorded an acceptable outcome. Keeping these statuses separate is an important control.
How can onboarding delays be reduced?
Clarify requirements, use conditional questions, assign owners, run independent reviews concurrently where permitted, automate reminders, define escalation rules, and eliminate unnecessary duplicate data entry. The objective is to remove administrative friction without removing necessary controls.
Should banking information be included in the main form?
It can be collected as part of the overall process when needed, but sensitive payment information should be handled through the organization’s approved secure process with access restricted to authorized personnel. The template should record payment-readiness status without unnecessarily exposing sensitive details.
How often should a vendor onboarding template be reviewed?
Review it periodically according to organizational risk, volume, and regulatory or process changes. It should also be reviewed when major systems, approval structures, vendor categories, or information requirements change.
Conclusion
A strong vendor onboarding template provides a repeatable framework for collecting information, verifying evidence, assigning responsibility, completing approvals, and activating suppliers. Its value comes from making the process clear rather than from making the document large.
The best design combines a practical baseline with conditional requirements. Vendor identity, contacts, services, financial setup, documentation, compliance, contracts, approvals, and activation should be connected through clear statuses and ownership.
Format should follow function. Excel can support structured tracking and analysis, Word can support narrative documentation, PDF can provide a stable printable representation, and online forms can improve supplier data collection and workflow routing.
Organizations should also treat onboarding as an ongoing management process. Accurate vendor records, controlled updates, expiration tracking, performance reviews, and documented changes keep the original onboarding information useful long after the supplier is activated.
When implemented thoughtfully, a vendor onboarding template becomes more than an administrative form. It becomes a practical operating framework that improves data quality, clarifies accountability, reduces avoidable delays, and gives procurement and related teams a consistent foundation for managing supplier relationships.
